UniFi Dream Machine (UDM)
Routing, firewall policy, DHCP, VPN access, and VLAN control.
INFRASTRUCTURE
A practical environment spanning routing, switching, wireless access, virtualization, container services, network storage, and secure remote access.
NETWORK ARCHITECTURE
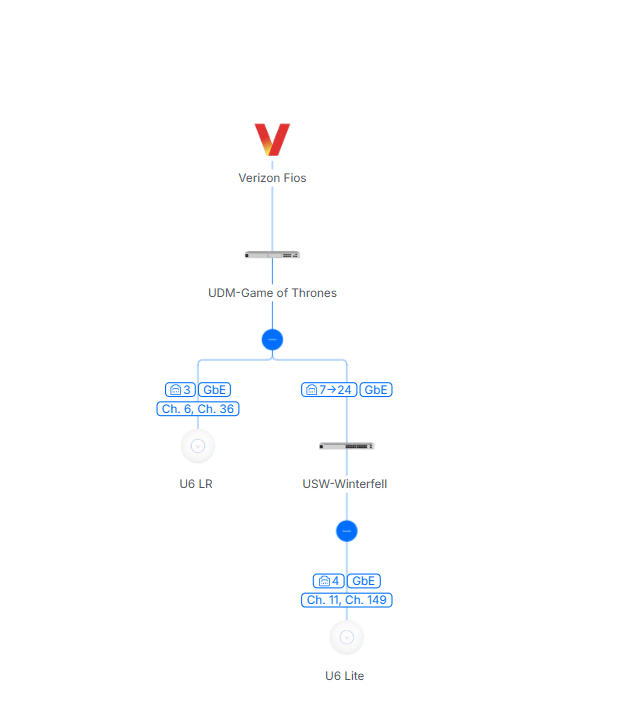
The network supports a three-floor home environment while separating trusted clients from IoT devices and keeping remote administration behind VPN access.
Routing, firewall policy, DHCP, VPN access, and VLAN control.
Central wired connectivity for endpoints and access-point uplinks.
U6 Lite and U7 Lite access points provide distributed coverage, with wireless expansion planned as needs change.
Separate VLANs reduce unnecessary access between personal systems and connected devices; mDNS is enabled only where discovery is required.
PROXMOX
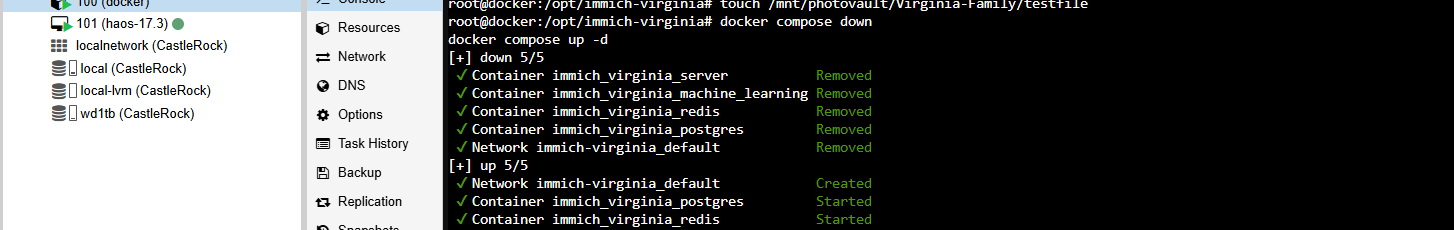
Proxmox VE hosts Linux container infrastructure and centralizes compute, networking, storage mounts, maintenance, and recovery.
STORAGE
Synology and QNAP systems provide centralized storage for media, backups, photo libraries, and application data.
SMB/CIFS shares support music, media services, home directories, and Sims backup workflows.
Dedicated storage for the Virginia photo environment with separate users, groups, and capacity planning.
Persistent mounts, permissions, reachability, and startup dependencies are documented because storage availability directly affects hosted services.
DOCKER
Application stacks are managed through Docker and Portainer, with supporting proxy, database, cache, media, monitoring, and file-management services.
SECURITY
The public portfolio describes the lab; it is not hosted inside the lab and cannot reach internal management systems.
Traffic between network zones is limited according to device and service needs.
Hypervisor, NAS, network management, and dashboards are not exposed publicly.
Approved applications use HTTPS through a reverse proxy rather than direct management access.
Public diagrams omit real addressing, credentials, serial numbers, and sensitive rules.